A practical environment for experimentation
The homelab brings personal and experimental services into a Docker-based environment. It combines service hosting with the networking and monitoring needed to manage that collection.
The original project includes media services as well as infrastructure tools. It is a place to work with the operational details around applications, rather than treating the application alone as the whole system.
Organizing access and visibility
Traefik provides a common reverse-proxy layer. BIND9 handles local DNS. Grafana and Zabbix support monitoring, while Homarr organizes access to the services. The project documentation also describes TLS configuration and access controls.
Keeping service definitions in Compose files makes the collection inspectable. The file-browser image in the gallery shows one such configuration file in the Homarr directory.
What the archive shows
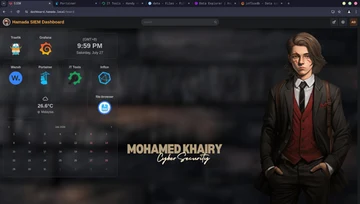
The gallery preserves the original application views and the old cover illustration. The cover is artwork; the interface screenshots document the actual lab. Existing masked areas in those screenshots are retained.
Scope
This is a personal lab for self-hosting and experimentation. Its original deployment is documented separately from the newer Kubernetes/red-team lab described in my CV. Their configurations and results should not be assumed to be interchangeable.